OSINT for GSOC Teams: Seeing Threats Before They Arrive
Most threats to executives and sites take shape in public first. Here is how GSOC teams can read that trail early and act on it.
Überblick über die Plattform
Erfahren Sie, warum Penlink der weltweit führende Anbieter von KI-gestützter digitaler Intelligenz und Ermittlungen ist
Penlink Academy
Your complete destination for Penlink training, with live sessions, on-demand modules, and certifications designed to give professionals the tools and confidence to succeed in real investigations.
A global security operations center protects people, sites, and operations across every region a company operates in. Most threats to all three take shape in public first, on social platforms, fringe forums, credential dumps, and local news. OSINT for GSOC teams is the practice of reading that public activity before it becomes an incident.
The risk lives in the gap between what is public and what the security team can see. Cameras and access logs show what already happened. Open-source intelligence shows what is still forming. As a result, it gives analysts early warning, real context, and reach across every region they cover.
Threats to corporate leaders have escalated quickly. After the December 2024 killing of a major health insurer’s CEO, companies moved fast to reassess executive protection.
A 2025 Goldman Sachs survey of 291 companies found that 27% now provide personal security for their CEOs. That share rose 59% in just two years.
Incident data tells the same story. A 2026 Security Executive Council analysis found that targeting incidents against executives doubled in 2025. Most involved physical activity, such as assaults, stalking, and protests. Cyber incidents, including threats, swatting, and account compromise, made up most of the rest.
Many of the warning signs behind these numbers appeared in public before any harm occurred. Therefore, GSOC teams that read those signals through OSINT gain the time to act.
Cameras, badge readers, and mass notification systems remain essential. However, they record events after they begin. A protest at the gate or a forced entry reaches the screen once it is already underway.
Commercial threat feeds help, but they often arrive late and read as generic. Vendors write them for a broad customer base, not for one company’s executives, sites, and regions. Consequently, analysts spend hours sorting noise and can miss the one signal that matters.
Hostile intent often leaves a public trail before anyone acts. A grievance post, a photo of a building entrance, or a planned demonstration can appear days ahead. OSINT gives the GSOC a way to pick up that trail while there is still room to respond.
Protective intelligence starts with exposure. Executives, facilities, and events all carry a public footprint that can include fixation language aimed at a leader, geotagged photos outside headquarters, or posted travel plans. Mapping the connections between accounts shows whether a hostile voice acts alone or belongs to a coordinated group.
Regional reach matters just as much. A GSOC answers for sites and people that headquarters may never see in person. Nearby crime, incoming storms, and unrest along a travel route all surface in open sources first. With that lead time, teams can reroute an executive or secure a site before a situation develops. That is the practical value of executive protection grounded in open-source intelligence.
Cyber threats belong in the same picture. Leaked credentials, doxxed home addresses, and exposed building details often surface online before a physical incident. In Allied Universal’s 2025 World Security Report, three-quarters of security chiefs said a disinformation campaign had targeted their company. Campaigns like these can put leaders at greater physical risk.
Because these signals are public, a GSOC using OSINT can track them alongside physical risk. A single view of both shows when an online threat starts moving toward the real world. For this reason, cyber threat intelligence increasingly sits beside physical security in the GSOC.
Running OSINT for GSOC operations at global scale creates a new problem. Every region, site, and executive adds signals, and no team can review them all by hand. Volume, not access, becomes the bottleneck.
Agentic AI changes how that work gets done. Instead of one tool answering one query, an agentic platform breaks a request into tasks. It then assigns each task to a specialized agent. Some agents collect, others triage, and the results come together in a single picture.
CoAnalyst360, Penlink’s agentic AI platform, applies this model to digital intelligence. An analyst states a question in plain language, and the platform plans and runs the research behind it. Recurring work, such as monitoring a region or an executive’s travel route, can run on a schedule. Reports then update as new findings arrive.
Furthermore, the analyst stays in the loop throughout. Each finding links back to its source, so the team reviews conclusions instead of chasing raw feeds. As a result, the same team can cover far more ground.
The first question in any incident is scope. Is the company the only target, or does the threat reach across the sector? Every decision that follows depends on the answer.
Delay carries a real cost. In Allied Universal’s 2025 World Security Report, surveyed companies lost close to $1 trillion in revenue to physical security incidents. Every hour spent scoping an incident is an hour the threat keeps moving. Therefore, OSINT for GSOC teams has to confirm early whether hostile chatter or exposed details are already circulating.
Most risk signals resolve to nothing. Clearing one quickly is a result worth reporting, but only if the reasoning holds up under scrutiny.
This is where auditable outputs matter. Because CoAnalyst360 keeps every output reviewable, a “no threat confirmed” finding comes with a clear record behind it. That record protects the person, saves budget, and shows leadership that the response matched the real risk.
Most threats leave a public trail, and the GSOC that reads it first sets the terms.
Request a demo to see how Tangles and CoAnalyst360 bring open-source intelligence into daily GSOC operations.
Most threats to executives and sites take shape in public first. Here is how GSOC teams can read that trail early and act on it.
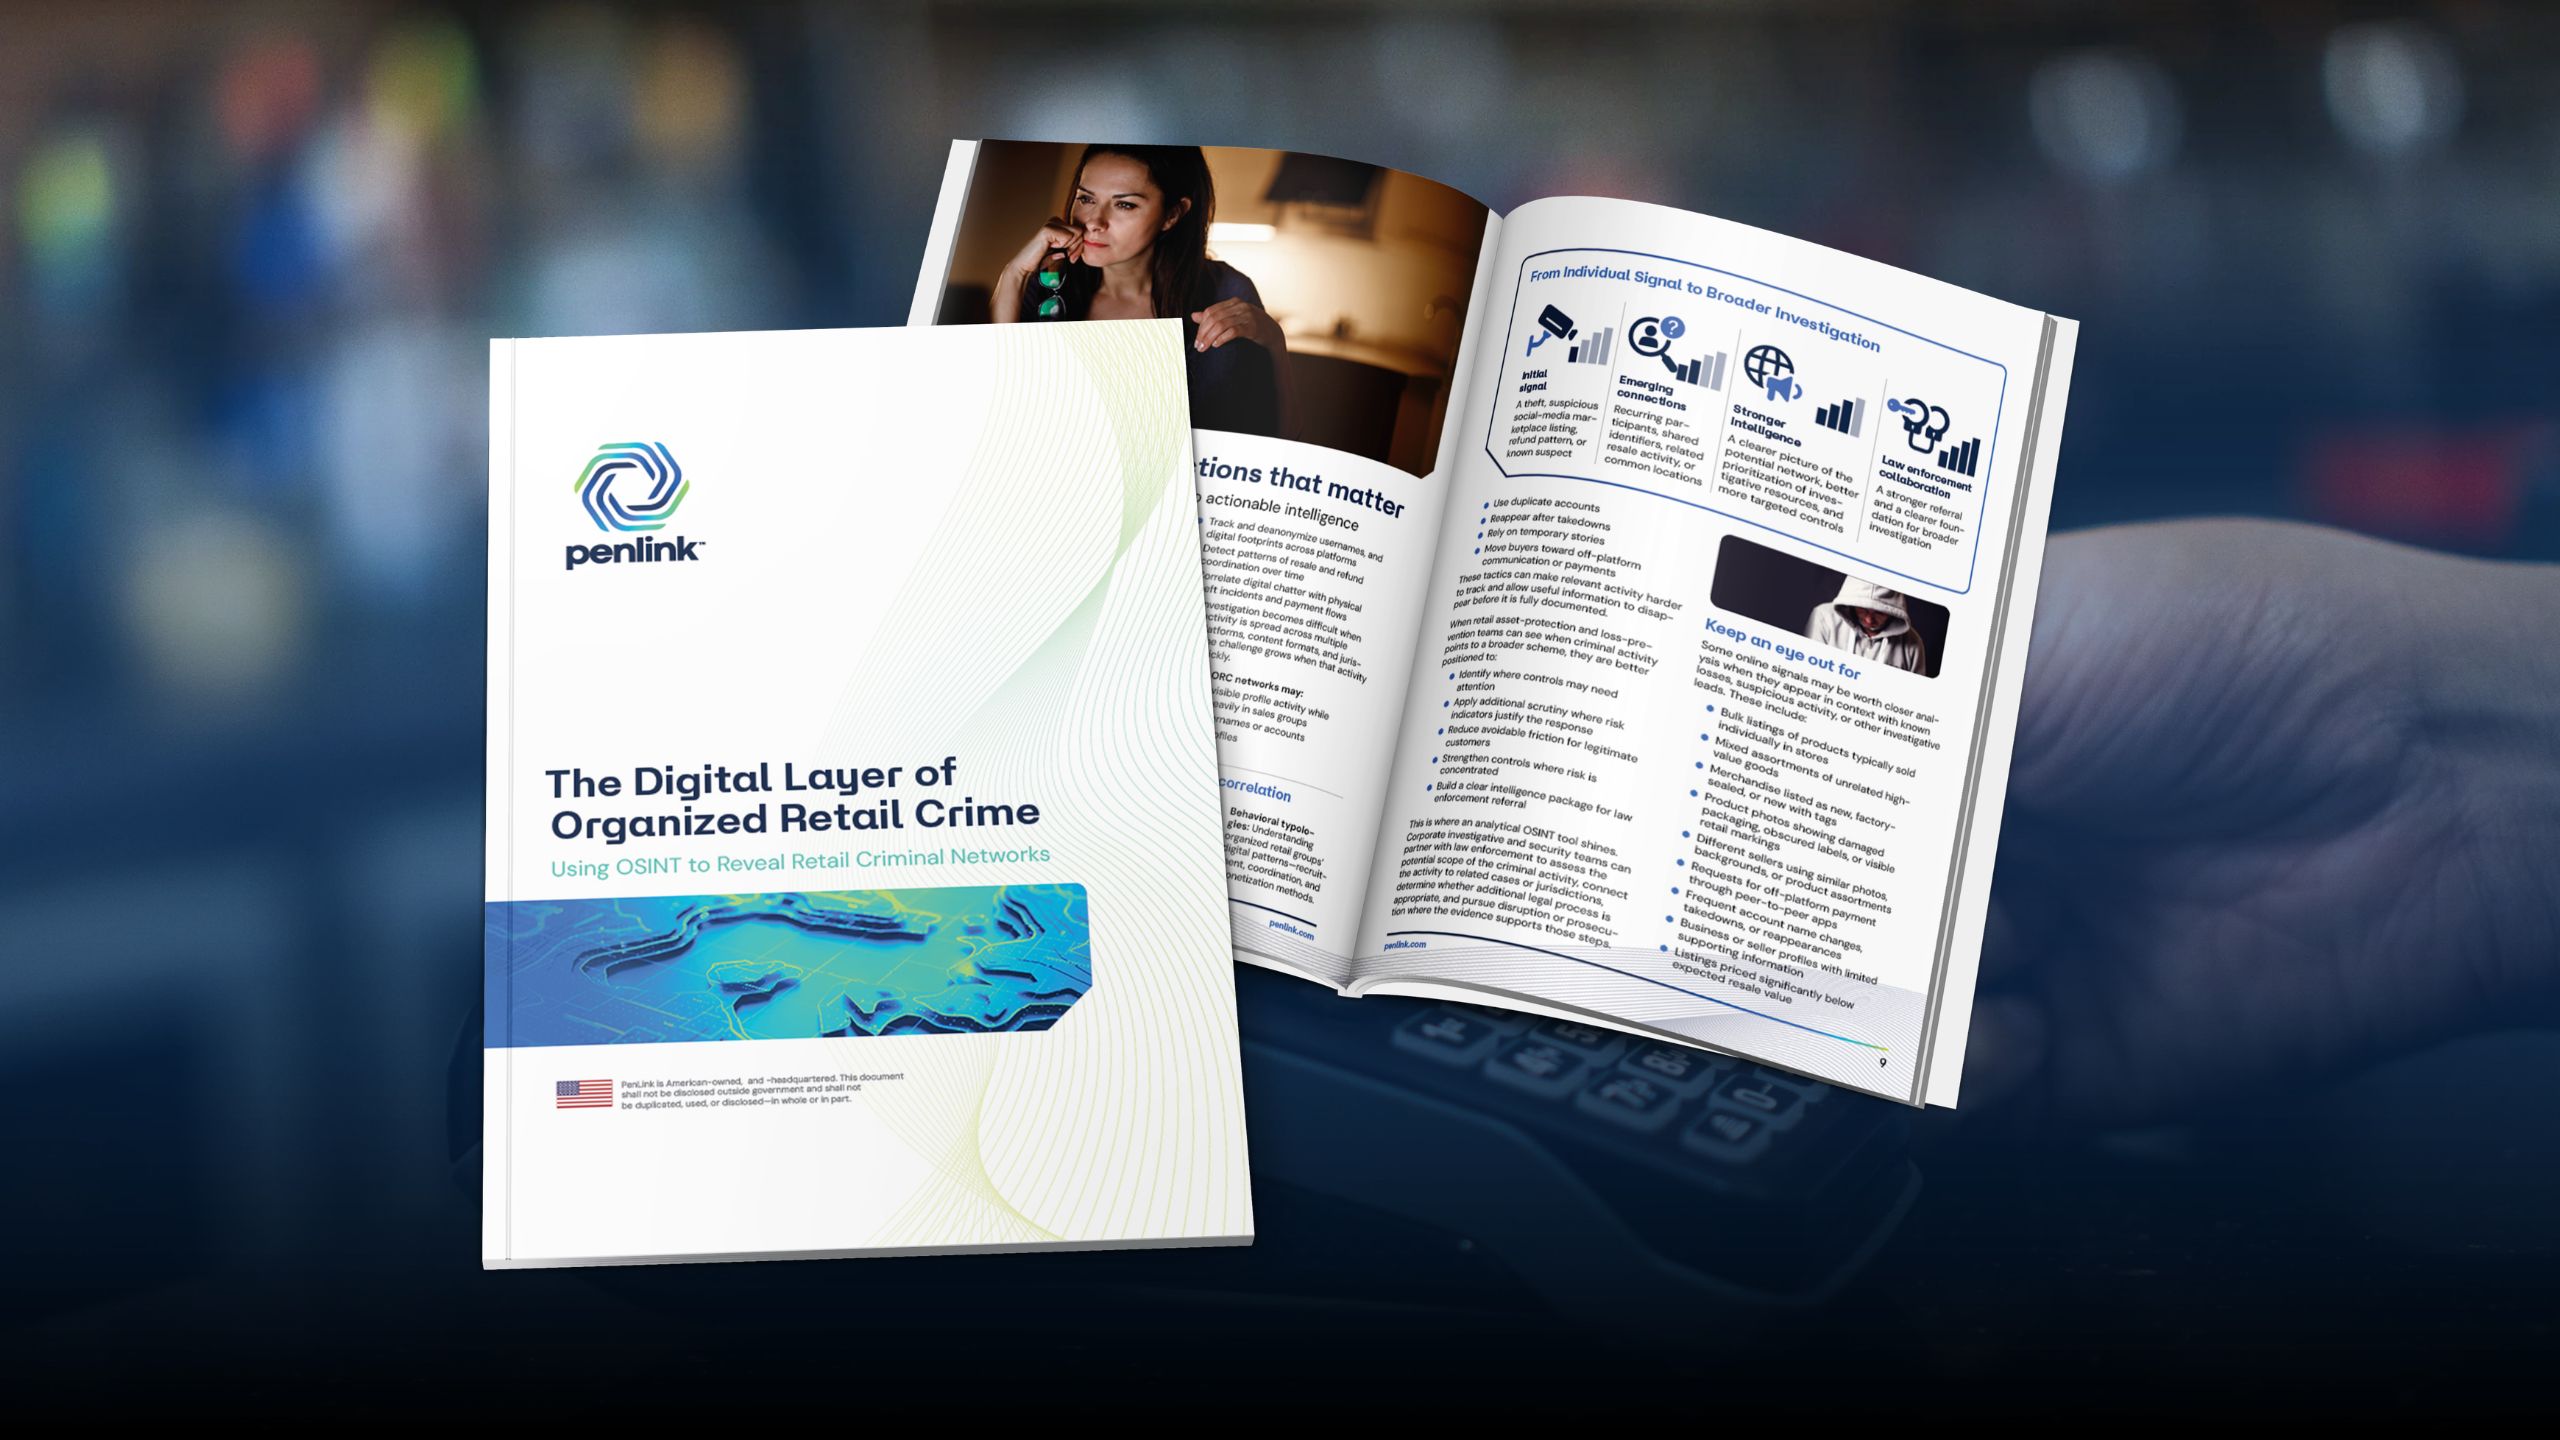
Organized retail crime networks move stolen goods and scale fraud through online marketplaces and messaging channels. This white paper shows how loss-prevention teams can connect individual incidents to the networks behind them.
Small boat crossings are the visible end of a much larger trade. This post looks at how open-source intelligence helps investigators see the networks behind them.
A single theft can be a one-off or the visible edge of an organized network. Retail and law enforcement teams need to know which one they are facing.
A coordinated operation across Volusia County targeted an alleged gang linked to shootings and overdose deaths, with more than 50 arrests expected.
Pen registers and live content intercepts operate under different legal authority. This post explains why getting the terminology right protects the collection and the case.