Your complete destination for Penlink training, with live sessions, on-demand modules, and certifications designed to give professionals the tools and confidence to succeed in real investigations.
With the access to digital information and AI technology available today, law enforcement agencies are facing a new reality: strong cases increasingly depend on iCloud+ evidence, not just forensic extractions from a seized phone.
For years, a mobile device extraction was considered the gold standard for digital evidence. It remains an important investigative tool, but investigators should not overlook the additional evidence found within cloud data, particularly Apple iCloud+.
Investigating Before the Phone Is Ever Recovered
One of the biggest advantages of iCloud+ is speed. Instead of waiting days, weeks, or even months to unlock a phone, or potentially never gaining access to it at all, investigators can begin developing leads almost immediately through lawful iCloud+ search warrants. In many investigations, they don’t even have the physical device when these searches begin.
Whether the phone has been destroyed, encrypted, or factory reset, or if it simply has not been located, cloud data allows investigators to continue moving the investigation forward.
For instance, when dealing with an overdose investigation, law enforcement agencies don’t have the luxury to wait. They need to identify suppliers, preserve evidence, and establish timelines while the case is still active. Phone data often becomes the evidence that ultimately proves who supplied the drugs, and the iCloud+ data can generate proactive investigative leads long before a physical device may ever be examined.
Sometimes the Cloud Holds More Than the Phone
Oftentimes, investigators find that iCloud+ contains evidence that never appears in a traditional forensic extraction, such as messages, photographs, and application data.
Depending on the user’s settings, many of these items have been recovered:
Historical photographs
Documents and credit-card images
Identification documents
FaceTime logs
Email histories
Device synchronization information
Historical IP address usage
Rather than viewing iCloud+ as a backup plan, investigators today should consider it a primary source of iCloud+ evidence.
The Entire Apple Ecosystem Becomes Evidence
In today’s world, users don’t live on a single device. Messages, notes, contacts, photos, documents, calendars, and communications often synchronize across iPhones, iPads, Macs, Apple Watches, and other Apple devices. A physical phone extraction only captures one of the subject’s devices.
By contrast, an iCloud+ warrant can potentially provide evidence generated across the whole Apple ecosystem, even when investigators never recover every device involved.
Now, instead of examining one phone, investigators can gain visibility into an entire digital footprint.
A Powerful Tool for Proactive Investigations
In today’s modern investigations, iCloud+ is much more than simply another place to retrieve evidence. It has become an investigative intelligence tool.
Using only identifiers such as a phone number or IMEI, investigators have identified suspects, located offenders operating internationally, uncovered fraud networks, and developed entirely new investigative directions that would never have been discovered through traditional methods alone.
With timely preservation requests under 18 U.S.C. § 2703(f), investigators can preserve cloud-based evidence early in an investigation, helping ensure that critical information is not lost while legal process is completed.
Rather than reacting after a phone is seized, investigators are now able to begin building cases while suspects remain unaware the investigation is underway.
The Best Investigations Use Both
Access to iCloud+ data should never replace forensic extractions. Instead, they should be seen as complementary investigative tools.
A forensic extraction captures what exists on a given device at that moment in time.
An iCloud+ return can provide historical backups, synchronized account data, communications, and evidence from multiple devices, often long before investigators ever obtain the phone itself.
The goal isn’t choosing one source over another. It’s building the most complete picture possible.
For agencies exploring how PLX Connect brings iCloud+ and mobile evidence together in one workflow, Request a demo.
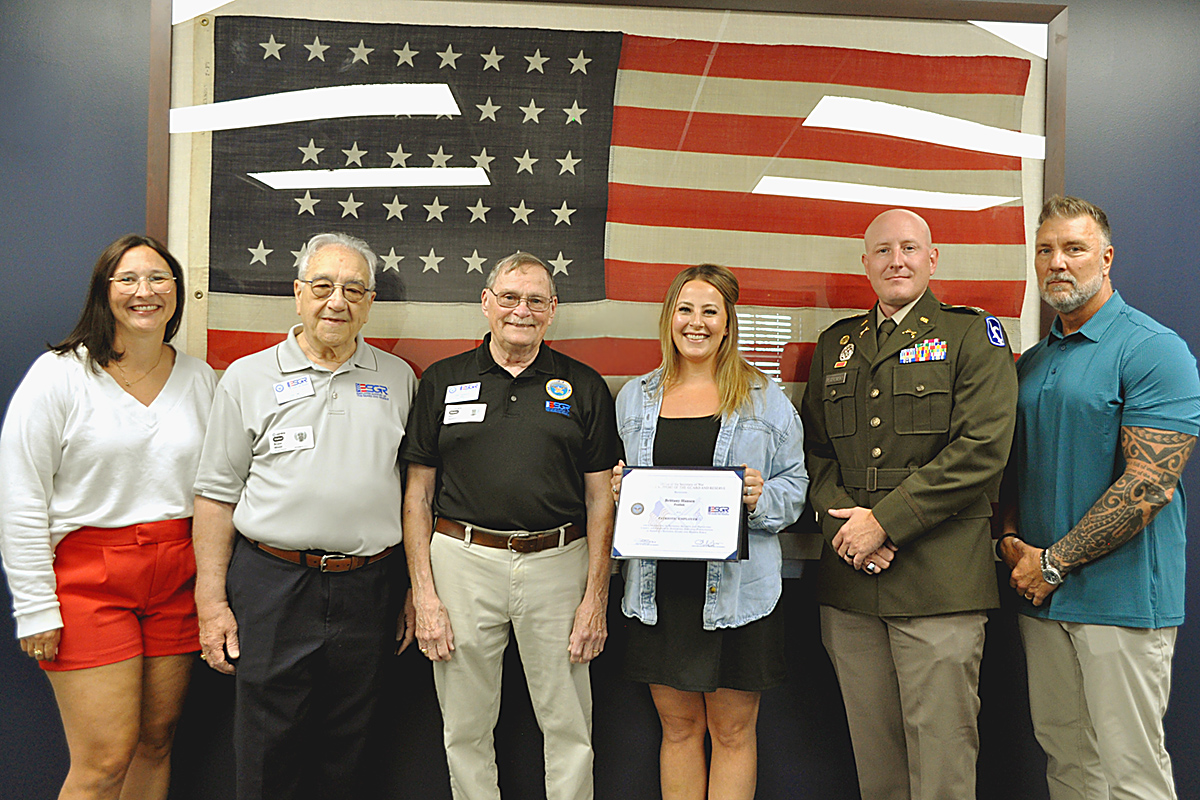
Penlink, a leading provider of digital intelligence solutions for law enforcement, national security, defense and enterprise organizations, announced today that Training Manager Brittany Hansen was presented with the Patriot Award from the Employer Support of the Guard and Reserve (ESGR), a Department of War program.
The Department of Homeland Security announced the results of a nationwide crackdown on human trafficking coordinated around the 2026 FIFA World Cup. Homeland Security Investigations (HSI), the DHS Center for Countering Human Trafficking, and federal, state, and local partners arrested 905 suspects and rescued 180 victims — 150 adults and 30 juveniles — across World Cup host cities.
The U.S. Marshals Service announced the conclusion of Operation Meridian, a month-long, multi-agency effort that located and recovered 79 reported missing and endangered children across Ohio, ranging in age from 6 to 17. Officials described it as the largest missing child operation in the state’s history.
A multi-agency investigation in Volusia County, Florida, has led to the dismantling of a major fentanyl and methamphetamine trafficking network, with 49 people arrested and hundreds of grams of narcotics seized.
The Nebraska State Patrol says a routine traffic stop earlier this month led to what investigators believe is the largest drug seizure in the agency’s history. Governor Jim Pillen joined NSP to detail the case, along with a second, unrelated stop that turned up stolen commercial equipment.
Foreign influence campaigns increasingly pair disinformation with cyber intrusion. This post looks at what that convergence means for investigators tracking coordinated state-linked activity.